 J
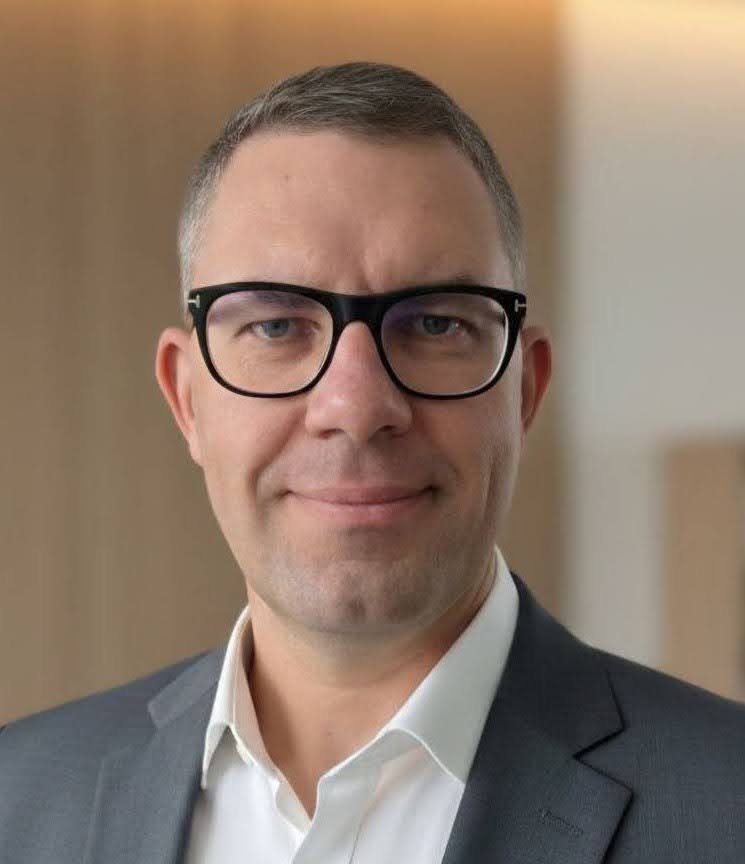
Jaroslav Řezník
— On the schedule —
The EU CRA vs. Community: Why You’re Safe, and How Stewards Help
The European Union's Cyber Resilience Act (CRA) is the first "horizontal" law to formally recognize the role of open source in the commercial software supply chain. While any new regulation at this scale naturally brings questions, the CRA actually offers an opportunity to standardize and elevate security across the entire industry. The law also promotes collaboration among all FOSS ecosystem players—contributors, maintainers, foundations, and commercial companies—by introducing the new role of the open-source steward. This session is an introduction to what the CRA really means for the community (spoiler: don’t be scared, you’re safe!) and how responsible stewards can help. In the first part, we’re going to strip away the jargon and explain exactly what the CRA is. We’ll cover the basics of the Act: who it applies to, what it asks for, and how it acknowledges the unique nature of open source. We’ll look at the specific exemptions designed to protect the "way we work," making it clear why individual contributors and community-led development remain in a safe, protected space. The second half of the talk introduces the concept of the Open Source Steward, a role designed specifically to support community projects. We’ll discuss how Red Hat, as a steward for Fedora, takes on the responsibility for high-level security policies, vulnerability reporting, and coordination with authorities. Finally, we'll take a look at how the OpenSSL Corporation and OpenSSL Foundation can navigate CRA requirements and stewardship in a very similar manner.
— Compositor's note —
Jaroslav is the Principal Program Manager guiding standards and regulatory initiatives for Red Hat's Product Security Compliance team. His 18-year tenure is defined by his unique versatility: he is as dedicated to his beloved Fedora open-source community as he is to ensuring Red Hat products meet strict regulatory demands. Beyond his work at Red Hat, Jaroslav serves on the ENISA Advisory Group and the OpenSSL Corporation Business Advisory Committee, helping to shape the future of cybersecurity globally and in Europe.